Thank you Nikos for having me on your show to talk about my favorite topic – AZURE! :D

We dove into a triumph from history where I was working with a customer to remove repetitive work and focus on sharing and internal reusability of proven Azure solutions within an enterprise.

website
[https://www.ndteknik.com/azure-triumphs-podcast/azure-triumphs-s01e04-magnus-martensson/]

announcement
[https://twitter.com/ndteknik/status/1632795252556791811]

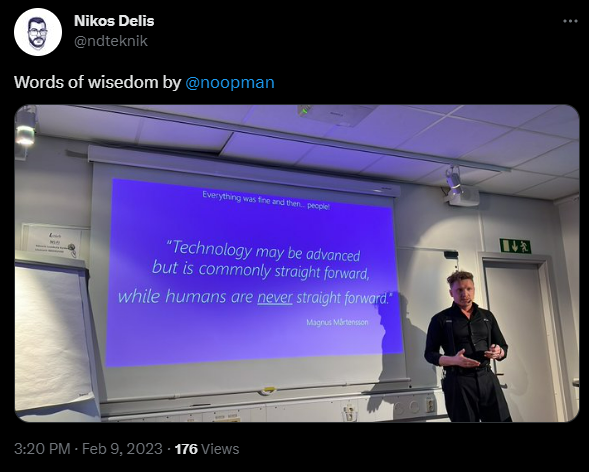
Also I like this snap from a recent presentation by the host himself:

Swetugg.tweet
[https://twitter.com/ndteknik/status/1623688184340021249]

Listen here:

spotify

applepodcasts


Comment Section

Comments are closed.


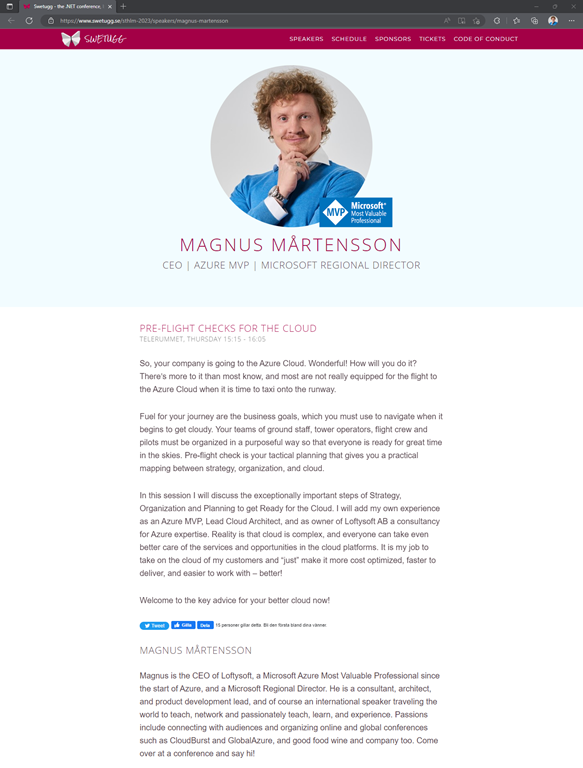
I spoke at Swetugg conference in Stockholm on February 9th 2023. This conference is EXACTLY what community passion is all about. The conference is organized and run by community speakers with such a wonderful setup. The best conferences are run by people who are speakers themselves, and whom in this case I am happy to call my friends.

My session was on a very important topic which seems to be coming very much into focus lately: All the things that matter getting ready for the cloud journey that are just next to technology! Technology may be complicated, but is commonly straight forward. People however are NEVER straight forward! This is a VERY important conversation to have about the world we live in as technologist enthusiastic about Cloud!

Magnus profile on Swetugg
[https://www.swetugg.se/sthlm-2023/speakers/magnus-martensson]

I hope to come back again to present at this awesome conference in my capital Stockholm! The conference was great. The food was great. The speakers were awesome, and I am proud to be one of them. Top level conference!

swetugg
[https://www.swetugg.se/sthlm-2023]


Comment Section

Comments are closed.


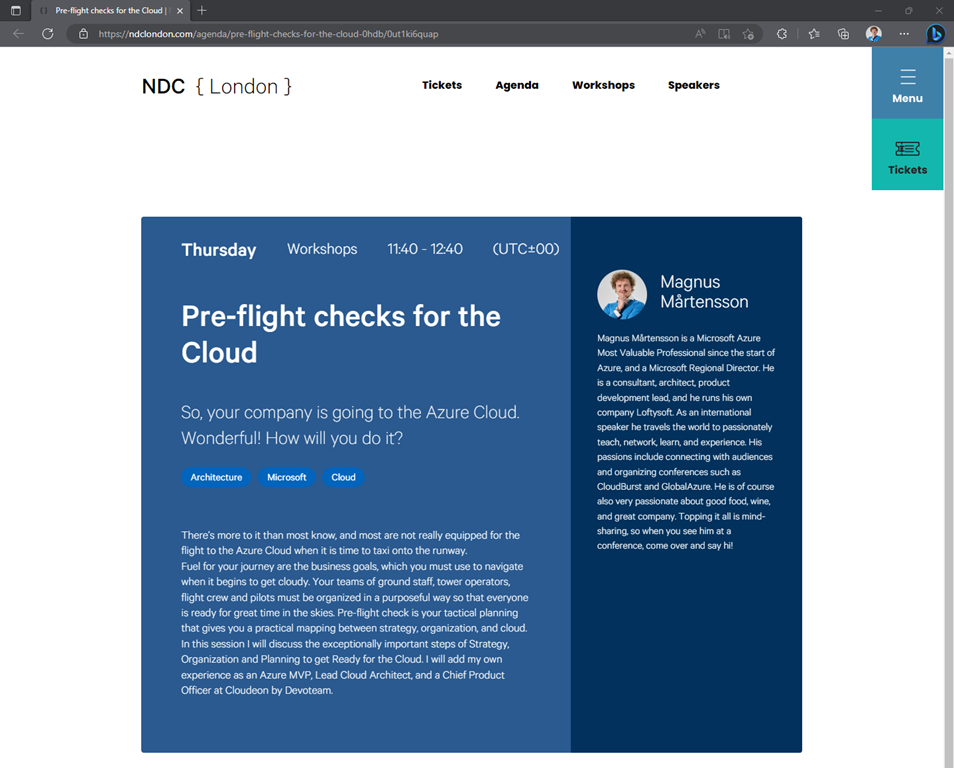
I spoke at NDC London on January 23-27 2023. The NDC Conferences crew are some of my very favorite conference organizers. Such warmth combined with professionalism and joy for their craft!

My session was on a very important topic which seems to be coming very much into focus lately: All the things that matter getting ready for the cloud journey that are just next to technology! Technology may be complicated, but is commonly straight forward. People however are NEVER straight forward! This is a VERY important conversation to have about the world we live in as technologist enthusiastic about Cloud!

Pre-flight checks for the Cloud
[https://ndclondon.com/agenda/pre-flight-checks-for-the-cloud-0hdb/0ut1ki6quap]

I hope to see you soon again in the world at one of the NDC conferences!

NDC London 2023
[https://ndclondon.com/]


Comment Section

Comments are closed.


(Original post on Microsoft Architecture Blog.)

You have your first Cloud Adoption Framework “Landing Zone” set up in the Azure cloud. Congratulations, your technical life will never be the same, and the sky is the limit to what you can now do. Having all the possibilities of the cloud, however, can be daunting. Like a cat at an open door, you may hesitate. Left paw first, or the right one, or simply jump right out there? Maybe just stay inside.

Now you must choose how to make your approach to the Cloud with the workloads in your portfolio. I assume you can choose between different workloads and timing, not limited to only very few workloads, and are not for example under an extreme time pressure that will force you to hustle with all you can muster into the cloud. You are reading this because you are about to select the optimal workloads suitable to start your company out and up into the cloud!

It is important to note that, although your company technical lead or cloud architect is heading the selection process, additional people in your company should be involved. Your business owners know the priorities for the current and future business both outside and in the cloud. Security officers may insist on moving data at a certain cadence, aligned with specific regulations. Even the HR department – often overlooked – might need to get involved. Why HR? If the first workload you migrate to the cloud is lacking cloud-experienced engineers on the team, it could impact the speed and accuracy of the ascent, as well as the attitude in your company regarding continued migrations.

There are multiple considerations to make when selecting your first workloads to go to the cloud:

  • Technical complexity – I recommend selecting something non-trivial, but also not the most complex solution you have! Pick something that you believe technically can have a start and a finish quickly, and that does not depend on complexities such as data access over a hybrid connection! Something less complex is the public corporate web site. It is not the most exciting application you have, but it is one of considerable value to the business. Stay away from using your core business application, with dependencies on other services in the company, as your first workload that goes to Azure. You want to start modestly and make sure you have something real running on Azure that you can measure for performance, and cost.
  • Security – Choose if you can, applications which have few users, or only internal users. Internet facing applications, with complex user access control, are technically more difficult to get right, and if migrated badly will cause a headache in your security department in the future!
  • Data complexity – A less data intensive application, where all the challenges of data compliance (personally identifiable information or sensitive data) is not the first thing with which you must deal!
  • Skills – Where do you have your rising cloud stars among the engineers in the company, and can you pick one of their workloads first? Any team with members that have previously used Azure or have someone Azure certified is a suitable candidate to start with. If your company does not yet possess any cloud experienced engineers, I self-servingly recommend taking your first workloads to Azure using advice from a cloud professional consultant. Initially in the cloud there is an abundance to learn. A focused investment in experience will pay back manyfold. Great engineers will eventually find a way, but engineers experienced at the task at hand will go more straight for the goal, faster. Your HR needs to be involved if your company is attempting a cloud ascent with no real cloud experience on staff!
  • Cost – Your organization needs to learn what Azure costs compared to pre-cloud IT budgets. Costs depend on level of auto scaling and other factors. If you can choose initial workloads that have medium complexity in terms of number of Azure resources and user scaling demands, it will make it easier to put financial controls in place.
  • Business value – If you migrate an application first that nobody in business cares about, you mind as well, in their eyes, not have done it at all. Pick something that matters to key people first!
  • Good model workloads – Workloads that go first to your cloud will serve as models for the batch of workloads that comes second. Consider elegance in the application and how easy they are to explain during show and tell. Maybe, do not choose Kubernetes or Machine Learning data platforms. Choose something that is easy to explain, where you can map applications clearly to Azure resources and show a solid set of basics for your future cloud adopting teams!

No matter which workloads go first, there is value to achieve from the initial migrations. You should take care to establish your key business cloud metrics that you can show to less technical managers. Non-technical folks (muggles) need something visual that excites them so that they understand that something is going on and can follow along. “How many workloads have we now migrated?” “How many new customers are using our cloud services?” It must be something/anything that matters to them. This helps with retention from C-level. Financial operation is another key. Satisfy “the bean counters” in your company with important numbers. You know the Excel-people. “How much is Azure costing month over month, and what is the consumption trend?” If you cannot demonstrate that you are in control of “how much,” you will come to rue the day the CFO comes knocking at the door of the development department fuming with a printed Azure bill in hand. Satisfy key stakeholders from the very beginning and they will not disturb you when you continue your technical Azure ascent!

As you work through this list while selecting the forerunners that blaze the path for your company service ascension to Azure, you need to decide what is the most prioritized consideration that apply to you and align your workload prioritization accordingly. I am sad to say that including technical stakeholders in the inception stages of the initial strategic planning when company suits decide to go to the cloud is not as commonplace as it should be. Make sure to align the strategic reasons “why” with the technical “how”! Head over to the Cloud Adoption Framework and delve into the Strategy and Plan sections before you proceed. Corporate reason for being in the cloud – your cloud strategy, and the method of approach – your plan, must be in good order before you actively adopt too many workloads into the cloud! When strategy and plan are in order, it becomes clear which important first cloud metrics you must establish as the first workloads go online! To better understand how key metrics in Azure work, and how to integrate them in your pre-cloud applications, please investigate the Well-Architected Framework, which has lots of references, guides and examples on how to configure your applications for reliability, cost optimization, operational excellence, performance efficiency and security. Exactly what metrics are the most important to your organization will vary based on your mileage. Let me give you a couple of real-world examples to highlight what I mean.

Recently, my firm was guiding a Cloud approach for a company that just had a security breech and had suffered data loss. It is so interesting that today companies consider a cloud first strategy to increase their security posture. I remember the early days of Azure, when Azure was “Windows Azure,” relevant and major objections from SecOps. Security was an adoption blocker. The Cloud was not compliant enough or proven to be secure enough. Today we experience the inverted argument – a move to the cloud increases security. Their number one, uncompromisable requirement was therefore security. We ended up putting extra effort into strengthening the cloud security skills of their IT department, and we did multiple reviews on their security. What was then critically important was to wire up the right security alerts to an active 24/7 monitoring call center, should an attack or security anomaly ever occur.

In another customer case, they started out toward Azure with a quite limited Azure budget. In this situation we were looking to generate buy-in from the business. They needed to get a couple of solid POC applications running in the Cloud, show the value and cost management, and then expand from there. While I very much appreciate that budgetary concerns sometimes must be a reality, it is worth mentioning that approaching the Cloud this way is an initially terribly slow process. You need to build an end-to-end full solution in the Cloud for the initially selected workloads, while ensuring – and proving, that the workload cost profile is optimal. It is a great learning for the teams involved in this initial cloud journey, because they learn so much about the Cloud, auto-scaling, good architecture, by being extra thorough to begin with. For this customer, the focus was on cost analysis and performance optimization.

Regardless of what metrics matter the most to you, future workload migrations and future innovations in the Azure cloud depend on how you select, and how you measure and report on the first workloads. Your second batch of workloads will follow the same ascent up to the mighty cloud above. Good luck!

Click on the following links to learn more about Well-Architected Framework, Cloud Adoption Framework and reference architectures.

About the author

Magnus Mårtensson is a Microsoft Azure Most Valuable Professional since the start of Azure, and MVP of the year in 2012. Additionally, though he does not work for Microsoft, he holds the title Microsoft Regional Director, which means an exceptionally close business relationship with his partner Microsoft. He is a consultant, architect, and product development lead, and an international speaker traveling the world to teach, network, learn, and experience. Passions include connecting with audiences, organizing online and global conferences such as CloudBurst and GlobalAzure, tasty food and wine, and great company. Topping it all is mind-sharing, so come over at a conference and say hi!


Comment Section

Comments are closed.


You need Just-In-Time (JIT) reasonable access for all relevant parties working with your Azure assets! Read along here as Magnus Mårtensson, CPO in Devoteam M Cloud Denmark and Microsoft Regional Director, walks you through the complex and powerful world of Privileged Identity Management (PIM).

In this article I bring you along for a deep dive into the specifics of Azure Active Directory Privileged Identity Management (PIM) and why it matters more than you think. 

Magnus-Azure-active-directory

Giving the wrong levels of access to your Azure assets and service environments is probably the leading cause of Cloud headaches. It is responsible for all kinds of downstream trouble including, but not limited to:

  • Environment drift – when anyone can modify any setting they presume should be modified. This leaves you with differing environments when you need them for testing. 
  • Bad actor – when an employee is disgruntled, malicious, or maybe even is spying on your company.
  • Human error – when someone for example accidentally picks the wrong database to run a change script on and were only able to do so because they had too much access in the first place. 
  • Stolen credentials – via stealthy social engineering like phone or email scamming or stolen hardware.

What you need is Just-In-Time!

As professional people, we do not want to make mistakes. And the best way to avoid making mistakes is to limit the risk of making them. At the same time, you need enough access to do your job at exactly the moment you need to, or else efficiency suffers, and your workday becomes cumbersome. What you need is for employees to have Just-In-Time (JIT) access, in the form of “least privilege” access, to perform only the specific tasks they themselves need to do.

In most cases, JIT means that a person does not have very much access at all. That means: no access to privileged roles that provide high security access, such as modifying production environments, or accessing production customer data. When someone needs access to a privileged work task, however, it is possible to elevate a dormant role to perform work in the protected areas.

“Least privilege” is a principle that states a person should have access to what they need to do their job, but no more. Bothering employees with having too much access as permanent assignments will often lead to mistakes that can carry a very high cost. This is not only very unnerving for employees, but usually leads to dissatisfaction, high employee turnover, data breech, and other negative outcomes. While people must be enabled in a timely manner, and need to feel empowered to do their job, my experience is that they do not want to have much more access than needed.

Nobody wins when everyone has access…

An old customer of mine had hundreds of customer databases. One database per customer environment. Because the company did not have a setup that enabled JIT and least privilege, they granted too much access to too many employees. It was bad to the extent that they in fact granted permanent database-server level access to support staff, including new hires, to 200 or more databases! Keep in mind that an ordinary support case would only require temporary access to just one database. As you can imagine the security situation, the data protection compliance, and the surface area for making a rookie mistake was horrible. Situations like this are so dangerous and completely unacceptable in any modern company.

The correct and powerful tools to stay safe and sound in your company while being empowered to effectively do the job and success is paramount. Enter stage left: Privileged Identity Management in Azure Active Directory.

What is AAD PIM?

The Microsoft Azure Active Directory (AAD) is the identity and access service underpinning all of Azure and many other services from Microsoft. In fact, a while ago Microsoft’s new “Windows Azure” Platform did not yet support any Active Directory services. We used to sign into Azure with non-corporate Microsoft Accounts to access corporate resources, because it was the only option available. AD services in the Cloud emanated instead from the Microsoft Exchange evolution we know as Office 365. 

When the Cloud AD service for office workers had hundreds of millions of daily sign-ins, the same service was also added to and modernized Microsoft Azure. Today we have one cloud-based Active Directory service in the Cloud called AAD to govern access to all Microsoft services.

The Privileged Identity Management features (PIM) of AAD are part of the premium service offering, which means they require a “P2 license”, which is a higher cost per user. The obvious question is if it is worth the extra cost? The answer is indisputably – YES! 

Why PIM is well worth its cost

PIM allows you to set up access that is not permanently active, but instead access that a user is eligible to activate when needed. A worker can have the admin access they need – to perform high security maintenance – only when the role assigned to them is activated. There are many features in PIM that make this a dream to work with:

  • Activation can require a logged justification from the user asking for access. 
  • All PIM activation activity is traced and support audits. 
  • Requests to elevate can have required manager review with the option to approve or deny the action. Even denied requests are of course audited. 
  • You can even connect a work item ID to an elevation request. 
  • When you activate an eligible role, it may be required to provide Multi Factor Authentication (MFA), for example using your mobile phone, to complete the request. This adds one additional level of security exactly where it is needed and prevents access with stolen account credentials.

Security when using PIM drastically increases, and user risk of making mistakes is drastically decreased.

The risks of moving with the front line

There are a few downsides with PIM to that you should be mindful about. One glaringly obvious one is that some of the features of PIM are still in preview in Azure, which means that they do not yet have a service-level agreement (SLA) from the supplier, Microsoft. Can you then use those features in your production areas? 

Many enterprises today have taken that step, but only you can assess if that is appropriate for you and your company. The positive spin on this is that the feature set of PIM is already rich and expanding, allowing you fine-grained control of user access management. Moving with the front line can generally be very beneficial and well worth the risks. 

The downside to the fine-grained control offered in PIM is that companies commonly find themselves challenged to make PIM work for them instead of becoming an administrative nightmare, or a roadblock for employees wanting their jobs. 

An automation silver lining?

But the automation story for PIM is still evolving and improving in this very moment. In fact, automating PIM configurations have moved from being an Azure concern only into becoming a broader Microsoft concern for all service offerings. 

This transition takes time, and in the meantime you as the end-user of PIM do not yet have a fully completed automation story. Downsides aside, AAD PIM is incredibly powerful and very well worth getting into and using to empower your organization. My recommendation right now for PIM is to proceed carefully yet resolutely and take advantage of PIM for your organization!

How to use PIM – a deep dive

Slightly more technically then, how does PIM work? Here is the high-level overview. First, an administrator with enough access, sets up PIM for a user. There is also an option to set up PIM for security groups and assigning many users as members to them that all get the same PIM configuration. I will leave that optimization for the next post. When a user has eligibility to activate a role, they need to make a request for activation. The request can be configured to require written justification upon activation, and it is time limited – automatically revoked. 

Additionally, which is a great feature mentioned above, it can be set up to require MFA to complete an activation. When the request is complete, and if approval is required, an email is sent to the responsible manager, who can review, approve, or deny the request. If the request is approved, the requester is notified of the approved access. The activation is ready to take place. The employee now has an approved activation request and can proceed to activate the role and access that comes with it. After work is completed, either the access expires on its own, or can be deactivated. This is particularly useful, because the reason for having permanent access is often that “we don’t have a process to manage revoking it”. All this activity is logged and can be audited.

Your guide to mastering PIM:

In essence the following challenges with PIM need to be overcome for you to successfully leverage the service:

  • Learning how to configure PIM access effectively and correctly. Again, the group management options are particularly good, but the automation story is currently lacking. 
  • Understanding the scenarios for PIM, where it makes a good difference, and how different configurations of the same can target different scenarios. Both examples are equally valid, supported by PIM, and quite different from each other: 
    • Access to Global Administrator Role – the highest AAD role – probably always needs to be justified, approved, and MFA secured. Each time this access is needed it must be for a specific reason, maybe even tied to a work order number. 
    • Managing user accounts – Create new users, assign them an O365 license, and assign SharePoint permissions is an administrative role that is also protected. This role, however, can possibly be activated without manager approval. It is still audited of course, and MFA can be required to protect employee data. Making a single activation to receive all three roles required, AAD User Administrator, License Administrator, and SharePoint User Administrator, just-in-time when needed, is certainly very beneficial.
  • Adapting your organization to learning to live with just-in-time roles and being effective doing so. There can be initial resistance when the company tightens security – “am I not trusted” – and “I don’t like change”. If PIM is loosely configured, it might not be as secure as required, but if it is very tightly configured it may be seen as an obstacle to being effective. The organization needs to adapt here, and PIM configurations need to be tweaked until they suit you well!

Change is rarely comfortable

That last point warrants some additional consideration. It is a story old as time – Who moved my Cheese* – where we need to be reminded that people generally do not respond very well to change. It is in the best interest of any company not to be careless with permanent access to critical systems. 

As pointed out, all bad things that can happen due to too much access, including data theft and security breaches, will eventually happen. It is only a matter of time, and you cannot afford that to happen! You have to think of your business value weighed against the uncomfortability of change. Of course, business value wins. At the same time, we need to be mindful that these changes may be hard won. Changing how people work is sensitive.

Getting started with PIM

There are a few straight forward steps to take to get started toward safer and more sound access control with PIM.

  • Start a small POC with a few users. 
  • Build the business case motivation for the AAD P2 licenses. 
  • Prepare the upskilling for employees along with the motivations why this change is.

Good luck and stay safe and sound in the cloud!

Additional resources:

Wikipedia:

Principle of least privilege

*Who moved my cheese?

Azure Active Directory Privileged Identity Management AAD PIM:

What is Privileged Identity Management?

Originally posted at: https://www.devoteam.com/expert-view/mvp-insights-safe-and-sound-in-the-cloud-with-privileged-identity-management/
Comment Section

Comments are closed.


π